Key takeaways:
- Choose a management approach that lets your staff issue and remove access across every affected door.
- Check credential technology, reader connections, and door behavior separately because improving one does not resolve the others.
- Compare installation quotes only after they identify retained equipment, required work, ongoing charges, and who handles unresolved items.
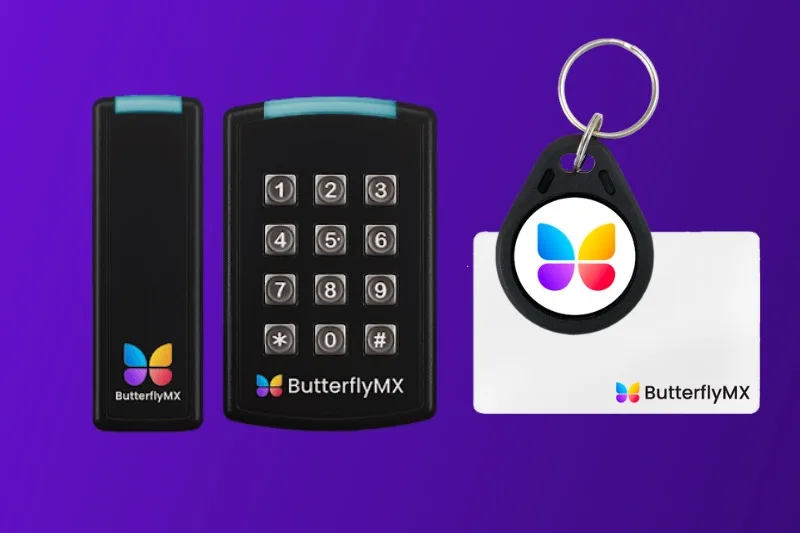
Card entry systems for buildings use a credential, reader, controller, and electronic locking hardware to grant or deny entry. Management tools maintain the permissions behind those decisions. If you manage an existing building, start by asking how your staff will keep those permissions accurate, not which reader looks newest.
A lost card or move-out makes the decision concrete. You need to identify all affected access, remove it, and establish what each relevant door will accept afterward. Replacing a reader alone may not solve that problem.
This guide explains how to choose a management approach, check security and outage behavior, and define the work an installer must quote. Those answers can help you decide whether to keep your key card system, upgrade part of it, or replace it.
This guide will answer:
- How card entry systems for buildings work
- Choose how staff will manage and remove access
- Identify the credential technology before judging security
- Check the reader-to-controller connection
- Separate outage behavior from safe exit
- Confirm what existing equipment can stay
- Compare installed scope and ongoing costs
Watch how ButterflyMX works:
How card entry systems for buildings work
A card access system checks whether a presented credential has permission to open a door. The credential is the card, fob, or other item used to request entry. A reader obtains its data, a controller checks permission, and electronic locking hardware responds.
The typical sequence, described in Silver Star Protection Group’s keycard access control guide, works like this:
- You present a card or fob to the reader.
- The reader obtains the credential data and passes it along for a decision.
- The controller checks authorization: whether the credential is active and has permission for that entrance.
- The locking hardware releases or stays secured according to the decision.
- Where supported, the system records the event for review. Available records and alerts vary by system and setup.
These are separate jobs, not necessarily separate boxes. Products may combine functions, and the access decision may happen in different places. Axis explains the roles of readers, controllers, and management software, including the connection that carries data between the reader and controller.
Management software lets staff maintain the permissions used in those decisions. Issuing a card is not the same as authorizing it: the assigned permissions must reach the part of the system that decides whether to open the door.
A reader alone is therefore not a complete key card entry system. Before replacing readers, identify whether your problem involves permission management, credential security, the reader connection, or door hardware. Start with permission management because it determines how your staff will run the system.
Choose how staff will manage and remove access
Choose a management approach by the work your building requires. Where will staff change permissions? How will doors receive those changes? Who maintains the equipment and software? A setup that suits one nearby door may create too much work across several buildings with frequent turnover.
Management architecture describes how you administer access. It is separate from credential type and wired or wireless connections. A cloud-managed system is not a type of card, and an on-premise system does not necessarily require programming at every door.
Compare standalone, on-premise, and cloud management
The table compares operating responsibilities, not security rankings. The standalone example comes from FPC Security’s single-door Visionis kits, which use local programming and need no server or software license. Those details apply to the listed kits, not every standalone product. Kisi’s system and cost guide provides context for local infrastructure and hosted services. These are vendor descriptions, not independent performance tests.
Swipe to compare →
A limited setup can be reasonable when local programming is manageable. As doors become more spread out or access changes become more frequent, the staff time needed to update each location matters more. Central administration may better fit that workload, but its interface alone does not prove that a change reached every door.
For either networked approach, ask the supplier how permission updates reach controllers and what happens when one is disconnected. A lost-card or move-out process shows why those answers matter.
Remove a lost card or departing occupant
Credential revocation means withdrawing access associated with a credential. Replacing a lost access card without disabling the old one leaves the missing card’s access unresolved. Your process needs to address both the old credential and any replacement.
Silver Star’s lost-credential guidance includes disabling credentials and reviewing records. Swiftlane’s building key fob replacement guidance adds request verification, appropriate permissions, and replacement testing. Use those steps to structure your process:
- Verify the report or move-out request and identify the correct account.
- Identify all assigned credentials and affected doors or areas. A departing occupant may have more than one credential.
- Disable the obsolete credentials or permissions through the supported administration method.
- Establish how each affected controller receives the change and what evidence shows delivery or effect.
- Review relevant access records, keeping their limits in mind.
- If a replacement is needed, assign the right access, test the replacement, and record its issue.
Suppose an occupant is moving out and has access to the main entrance, parking area, and amenity space. Removing only the entrance permission would leave the other areas unaddressed. First identify all assigned credentials and areas, then track removal across each one.
Use this planning aid for each affected area. It helps organize supplier answers and follow-up work; it is not a tested acceptance procedure or a substitute for system documentation.
In the move-out example, create separate entries for the entrance, parking area, and amenity space. Do not copy one result into the others unless the documented system behavior supports it. One dashboard may manage all three areas while leaving a delivery question at one controller.
If a controller is disconnected or delivery status is unknown, a completed dashboard action does not establish what that door will accept. Ask the supplier which permissions remain usable, how update status is reported, and what method establishes completion. Record the unresolved condition against that door and assign a named administrator to follow up. There is no universal revocation time that replaces these answers.
A genuinely lost card cannot be presented at a reader to test rejection. Instead, request supported delivery or status evidence and, where appropriate, a supplier-led demonstration using an available credential. Have the supplier explain what the evidence establishes for your system. Testing that a replacement works does not prove that the missing card is rejected.
Keep permissions accurate after installation
Access removal is one part of ongoing administration. In its operating guidance for key card systems, Kastle recommends clear credential-issuing and deactivation processes, periodic permission reviews, time-limited visitor or contractor access where supported, and assigned maintenance responsibility. This is vendor operating advice, not measured evidence of failure rates.
For your building, name who issues credentials, who handles move-outs, and who reviews permissions when an occupant’s role changes. Include visitors, deliveries, and after-hours contractors in the policy. Where the system supports expiry, decide who sets and reviews it. Software does not remove the need for someone to own these tasks.
Shared buildings may divide authority between owner-controlled common areas and tenant-controlled suites. If that applies to your property, evaluate who can view and change each group’s permissions and records. Ask how the proposed system keeps those responsibilities separate rather than assuming every product supports your authority model.
Access records can help with reviews, but they show credential events, not proof of which person entered. A shared or cloned credential can appear under the assigned account. Tailgating, when someone follows an authorized person through a door, can allow entry without another credential event. Record detail and retention also vary. These limits make it important to understand the technology inside the credentials you issue.
Identify the credential technology before judging security
Some building access credentials can be copied, including legacy 125 kHz HID Prox. Card, fob, and badge describe physical formats, not security levels. RFID describes a radio-based method, and frequency alone does not establish resistance to copying.
Find the credential family and generation
Start with purchasing records, system documentation, or your installer. Obtain the credential and reader model information, then identify three details: operating frequency, credential family, and generation. The family names the technology; the generation identifies a version within that family.
Telaeris’s HID-focused credential guide explains differences among legacy prox and higher-frequency families. Its identification guidance is not a dependable visual audit of every installed card. An HID marking or a 13.56 MHz label is not enough to establish what protection your building uses.
This information matters for replacements as well as upgrades. A key card and key fob may look different while using the same technology. Changing their shape does not establish stronger security or confirm that they will work with your readers.
Compare legacy prox, smart cards, and magstripe
Telaeris describes legacy 125 kHz HID Prox as transmitting credential data openly when powered by a reader, making the data copyable. Higher-frequency families and generations differ in their protections. Its guide distinguishes older MIFARE Classic and legacy iCLASS from newer technologies, so the broad label “13.56 MHz smart cards” does not describe one security level.
If an installer recommends smart cards, ask for the actual family, generation, and supported reader configuration. Those details are more useful than a general promise of “encrypted cards.” They let you assess the proposed equipment rather than apply a claim about one technology to an unidentified system.
Magstripe has a different daily-use tradeoff. Avigilon’s key card guide describes contact wear and reading problems that can lead to repeated swipes or replacements. Consider that handling burden separately from the family-specific cloning risks of contactless credentials.
Cloning and relay attacks are also different. Cloning copies credential data; a relay forwards a live exchange. A 2023 research preprint abstract reports a laboratory relay demonstration against HID Seos. That specific example does not establish a weakness in all smart cards or current firmware. It does show why resistance to copying and resistance to relay are separate questions.
Consider PINs, mobile access, and other entry methods
Cards do not have to be your only entry method. Avigilon describes alternatives and complements including PINs, mobile credentials, QR codes, and biometrics. Their usefulness depends on your building’s needs and the proposed system.
PINs avoid issuing physical credentials, but people can share them. Mobile credentials offer a phone-based option, but need compatible equipment and a clear explanation of offline behavior. Do not assume either cards or phones will work through every outage.
Temporary QR access may suit visitors if its validity and permissions can be controlled. Biometrics require an assessment of suitability, cost, and privacy. A mixed approach can serve different needs without making phones or biometrics a required next step.
No credential choice alone prevents sharing or tailgating. It also does not settle how data travels from the reader to the controller. That connection is the next part of the security review.
Check the reader-to-controller connection
Wiegand and OSDP describe the reader-to-controller connection, not card types. According to Axis’s comparison of Wiegand and OSDP, Wiegand sends data one way without encryption or protocol-level reader supervision. OSDP supports two-way supervised communication and AES-128 Secure Channel encryption.
Reader supervision helps the system monitor the reader connection rather than just receive credential data. The Security Industry Association’s OSDP information provides standards context, but a standard does not prove how your equipment is configured.
A proposal saying “OSDP supported” leaves a key question unanswered: will Secure Channel be enabled? Ask the installer to document compatible reader and controller support, the enabled configuration, how encryption keys are protected, and who manages them.
Axis describes two migration paths: replace the reader with a compatible OSDP reader connected to an OSDP-capable controller, or use a Wiegand-to-OSDP converter. A converter can protect communication toward the controller, but it does not change the credential technology.
Do not treat a converter as proof that the whole path is protected. The arrangement suggests a remaining reader-to-converter segment that needs separate assessment; Axis does not establish its protection in every installation. Have the installer show the actual segments and document the protection on each.
A stronger credential and a protected reader connection address different risks. Even together, they do not establish what happens during an outage or how occupants leave the building.
Separate outage behavior from safe exit
Ask what happens during each type of outage
Fail-safe means the locking hardware releases when power to the lock is lost. Fail-secure means it remains secured when lock power is lost. FPC Security’s lock descriptions illustrate the distinction with electromagnetic locks and fail-secure strikes.
A building power outage is not necessarily a loss of power at the lock because backup power may keep hardware energized. Internet loss is different again: it does not tell you whether the controller or lock still has power.
For each relevant door, have the supplier document these conditions separately:
- Internet loss: Which credentials remain accepted, and can permission changes reach the door?
- Local-network loss: What changes if the controller loses its local connection while other services remain available?
- Controller failure: How does the locking hardware respond if the controller cannot make or communicate decisions?
- Lock-power loss: What is the lock’s fail mode, and what backup power is specified?
For every condition, obtain answers about accepted credentials, permission updates, lock behavior, and equipment that remains powered. A cloud or on-premise label, or a general “works offline” statement, does not answer all four.
Have the complete exit arrangement assessed
Egress means leaving a building or space. A lock’s fail mode does not establish whether the complete exit arrangement meets applicable requirements. Have qualified professionals assess the door arrangement, adopted code, occupancy, local amendments, backup power, and exit-release provisions. Involve the authority having jurisdiction, the body responsible for local approval, where applicable.
For example, the Illinois-adopted 2021 IBC sensor-release provision reproduced by UpCodes includes multiple release and safety conditions. An included push-to-exit button alone does not demonstrate compliance. Sensor release and door-hardware release are distinct arrangements, not interchangeable labels.
Campbell Code Consulting’s guide to locking egress doors shows that section numbers and permissions change across code editions. Do not treat one section number or kit description as nationwide approval. Have professional findings and supplier answers included in the door survey and proposal instead of attempting electrical or compliance tests yourself.
Confirm what existing equipment can stay
Existing equipment may stay when the installer confirms that it is compatible with the proposed system and suitable for the door. An access control retrofit is therefore not simply a choice between keeping everything and replacing everything.
Request a survey covering credential and reader models, controller or panel support, reader interfaces, wiring condition and suitability, locks, power, and the door and exit arrangement. The migration paths described by Axis show why reader and controller compatibility must be assessed together. The credential and exit reviews address other parts of the same project.
Ask the installer to label each item so you can understand the proposed work:
- Retain: Document compatibility with the proposed system and suitability for the door.
- Replace: State the reason and identify the replacement work included in the proposal.
- Unresolved: Name the remaining check, the person responsible, and how it will be resolved before approval.
These are planning labels, not inspection certifications. A note saying “reuse existing readers and wiring” is incomplete if no one has confirmed the models, condition, and suitability of that equipment.
A staged migration may let you upgrade in steps. Alongside compatible reader replacement or converters, Telaeris describes multi-technology credentials that can serve older and newer readers during a transition. Actual card, reader, and panel compatibility still needs confirmation.
Keeping legacy technology usable can also preserve its risks. One badge working throughout the transition is convenient, but it does not prove the whole system has gained the protection of its newest component. Ask the installer to explain both the transition and the intended final setup.
Carry every retained item, replacement, unresolved assumption, and responsibility for confirming the work into the quote. Otherwise, a lower total may simply leave out work another provider included.
Compare installed scope and ongoing costs
Access control installation cost per door depends on equipment, door work, cabling, power, labor, configuration, and services. The useful budget question is what it will cost to deliver your building’s documented requirements, not what a reader or hardware kit costs by itself.
Separate one-time work from ongoing obligations
Kisi’s cost breakdown separates components, installation, configuration, and recurring services. Use those categories to request an itemized installation quote instead of treating a broad per-door figure as the price of a complete installed system.
One-time costs may include readers and controllers, locking hardware, door preparation, cabling, power supplies, installation labor, configuration, and work to confirm agreed functions. Identify applicable permitting too. A hardware kit does not account for all project work, even when it contains a reader, lock, and exit device.
Then separate recurring licenses or service fees from replacement credentials, support, and maintenance. Credential replacements may arise as needed rather than on a fixed schedule. For each obligation, record who handles it, how it is charged, and what is included.
Compare proposals for the same doors, functions, support, and time period. Distinguish shared infrastructure from per-door charges as well. A shared controller still belongs in the comparison even if it is not priced separately at each door.
Return mismatched proposals for clarification
Use this worksheet to collect entries from each proposal. It is a comparison aid, not an estimating model. Keep quantities, amounts, included work, and responsible parties visible instead of reducing each proposal to one total.
Swipe to compare →
Suppose one proposal includes lock and door work while another excludes it. The second total is not yet a lower price for equivalent work. Ask that provider to price the missing work, or have both proposals identify the separate work and who will deliver it.
The same applies to ongoing services. If one proposal states service charges and another leaves them unstated, a blank does not mean there is no charge. Return the proposals for clarification until you can compare their inclusions, exclusions, and responsibilities.
The right choice should address the operating problem that started the project. A suitable existing system may need clearer administration rather than replacement. An upgrade or replacement should resolve identified gaps, not leave permission delivery, compatibility, or maintenance ownership to be decided after approval.
When a cloud-managed option fits
If your requirements point toward hosted management and multiple entry methods, ButterflyMX is one option to evaluate. Its cloud-based access control system offers smartphone, fob, key-card, and PIN entry.
Apply the same project questions to ButterflyMX as to any provider. Confirm the proposed credentials, reader connections, equipment compatibility, and disconnected-controller behavior for your building rather than assuming those answers from the cloud-managed label.
Frequently asked questions
Is a key fob different from a key card?
They are different physical formats, but they may use the same credential technology. Identify the family, generation, and reader compatibility before judging security. Changing from a card to a fob alone does not establish stronger protection.
Can a lost card be tested after it is disabled?
A genuinely lost card is unavailable to present at a reader. Ask the supplier what delivery or status evidence establishes removal for your system. A planned demonstration with an available credential may help explain the process, but testing a replacement does not prove rejection of the missing card.
Do access logs prove who entered the building?
No. They record credential events, not proof of personal entry. Someone may share or copy a credential, or follow another person through a door. Records remain useful within those limits; their detail and retention depend on the system and configuration.
Does an included exit button make a card entry kit compliant?
No. A button is only one part of an exit arrangement. Requirements depend on the adopted code, occupancy, door arrangement, and local amendments. Qualified professionals and the relevant authority should assess the complete arrangement, including whether sensor release or door-hardware release applies.
Can one credential work during a staged upgrade?
Some multi-technology credentials can work with older and newer readers during a transition. Have the installer confirm the actual credential, reader, and panel compatibility. Continued acceptance of legacy technology may preserve its risks, even when the same badge also supports newer readers.
Before deciding to retain, upgrade, or replace your card entry system, settle four questions: who owns permission removal, which doors are affected, what establishes completion, and which compatibility, outage, or project questions remain unresolved.
Keep a suitable existing setup when it meets those needs. If it does not, give installers the documented gaps and request proposals with clear responsibilities. If hosted management and multiple entry methods fit your requirements, explore ButterflyMX cloud-based access control as a next evaluation step.
Get your free quote!
Fill in the form below, and we'll email you right back.
Want a free quote?
Fill in the form below, and we'll email you right back.
Redirecting you in 5 seconds.