Key takeaways:
- Cloud security and on-premise security solve different operational problems. Neither is automatically safer; configuration, governance, monitoring, staffing, and recovery planning matter more than the hosting model alone.
- Cloud systems usually move more cost into subscriptions and operating expenses, while on-premise systems often require more upfront infrastructure, maintenance, and internal support. The useful comparison is total cost over time.
- Hybrid security can give properties cloud-based administration with local controllers or cached endpoints, but continuity and migration depend on product design, hardware compatibility, power, and documented offline behavior.
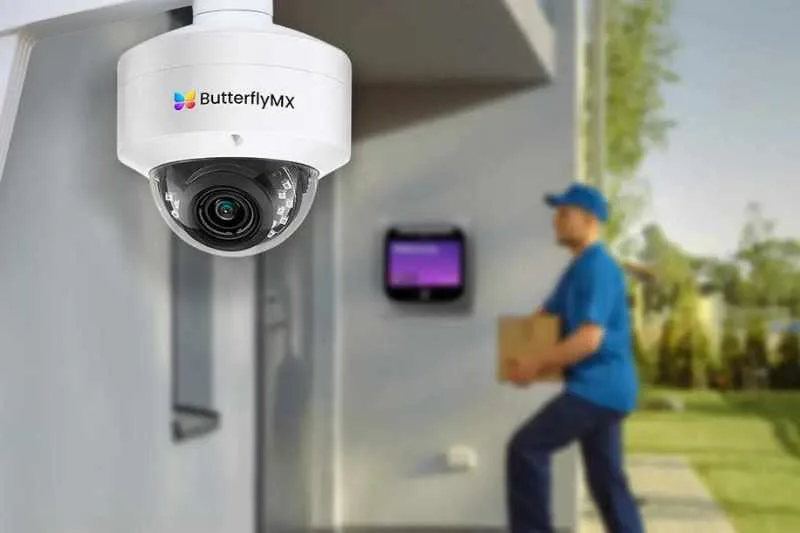
The choice between cloud security and on-premise security becomes real when a door needs to unlock, a resident needs access, an auditor asks where data is stored, or a site loses internet service. For managed properties, this decision affects more than software hosting. It can shape access-control administration, credential management, maintenance work, outage planning, compliance evidence, and how easily a portfolio can grow.
Cloud security uses provider-hosted infrastructure and a shared responsibility model. On-premise security keeps more infrastructure and day-to-day operational responsibility with the property organization or its service partners. One model is not automatically safer, cheaper, or more compliant than the other. The better fit depends on your staff, existing equipment, budget model, compliance obligations, connectivity, and required offline operation.
For many properties, the practical answer is not purely a cloud or purely an on-premise access control system. A hybrid model can combine centralized cloud management with local hardware that continues to support defined access functions. The sections below explain how to compare those options without relying on blanket claims.
This guide will answer:
- What cloud security and on-premise security mean
- How responsibility changes by deployment model
- Cloud security vs. on-premise security: key decision factors
- Is cloud or on-premise security safer?
- How reliability and internet outages affect physical security
- How hybrid security supports continuity and phased migration
- How to choose a model for each property and portfolio
- FAQs
Watch how ButterflyMX works:
What cloud security and on-premise security mean
Cloud security relies on computing resources hosted by a provider and accessed over a network. The NIST definition of cloud computing describes on-demand network access to shared, configurable resources that can be rapidly provisioned with minimal management effort. In practical terms, cloud security may include provider-hosted applications, centralized administration, identity controls, logs, and data services.
On-premise security keeps the servers, applications, or core management environment at a property or in an organization-controlled facility. That gives the organization more direct control over infrastructure. It also means the organization, its IT team, or its service partners must handle more maintenance, monitoring, backup, patching, and recovery work.
Physical security adds another layer to the comparison. Access control, video intercoms, credential readers, keypads, doors, gates, elevators, and local controllers are physical systems at the property. A cloud-managed access-control system can still use local hardware at the building. An on-premise system can still connect to remote services or outside integrations.
This is why cloud security vs. on-premise security is not just an IT hosting question for property teams. It is also a question of who manages access, where permissions live, how local endpoints behave during an outage, and what the property can support over the full life of the system.
How responsibility changes by deployment model
The core cloud concept is shared responsibility. In many cloud services, the provider protects the infrastructure layers defined in the service and contract. The customer still owns important duties such as administrator access, user permissions, configuration choices, data governance, and audit practices. A cloud versus on-premise security comparison makes the same point: moving infrastructure to a provider does not move every security duty away from the customer.
On-premise deployment shifts more of that work back to the organization. The property owner, operator, IT team, security team, or service partner may need to harden servers, apply software updates, monitor logs, maintain backups, respond to incidents, and test recovery procedures. Direct control can be useful, but only when the organization has the staffing, process, and budget to use that control well.
What property teams still own in the cloud
- Approving administrative roles and limiting access to people who need it.
- Removing access when residents, employees, vendors, or contractors no longer need entry.
- Reviewing configuration changes, audit records, and integration permissions.
- Understanding where access data is stored and what the provider contract covers.
- Testing incident response and recovery procedures that involve property operations.
The dividing line is not always obvious. A provider may handle infrastructure uptime while the property still controls who can change door schedules, issue credentials, or review event history. Ask for a written responsibility matrix before assuming that a cloud subscription or a local server answers every operational question.
Cloud security vs. on-premise security: key decision factors
The fastest way to compare these models is to look at what changes operationally. The table below is not a scorecard. A cloud advantage can disappear if permissions are poorly managed. An on-premise advantage can disappear if local infrastructure is not patched, monitored, or backed up. Read each row in light of your staffing, existing hardware, provider scope, and required offline continuity.
Cost is a good example of why the answer depends on context. Cloud systems often reduce the amount of customer-owned hosting infrastructure and shift spending toward recurring service fees. On-premise systems often require more upfront infrastructure investment and more internal support. Neither model is automatically less expensive. A useful total-cost comparison includes installation, local infrastructure, subscriptions, staff time, maintenance, upgrades, support, backup and recovery, downtime exposure, and migration. Industry comparisons from Avigilon and Acre Security also frame cost, control, scalability, and maintenance as context-dependent tradeoffs.
Compliance works the same way. A hosting label does not make a deployment compliant. A property must look at the actual obligation, data flows, data-residency needs, configuration, audit controls, and provider documentation. ISO/IEC 27001:2022 is an international standard for information security management systems, but a vendor certificate is not an automatic guarantee that a customer deployment satisfies HIPAA, GDPR, PCI-DSS, or another requirement. Certificate scope, configuration, and customer procedures all matter.
For access control, centralized cloud administration can be valuable when a property needs to manage many residents, staff members, vendors, doors, or sites. But that value depends on fit. A property with specialized integrations, strict data-residency requirements, limited connectivity, or strong internal IT capacity may weigh the tradeoffs differently. This overview of cloud-based access control benefits can help frame the operational reasons a property might consider a cloud-managed model without treating it as the default answer.
Is cloud or on-premise security safer?
Neither cloud nor on-premise security is universally safer. Security depends on implementation quality, configuration, identity and access controls, governance, monitoring, patching, backups, incident response, and recovery capability. Infrastructure location alone does not prove security maturity.
Cloud can be the safer choice when the provider has strong infrastructure controls and the customer configures the system well. It may also give smaller teams access to specialized infrastructure, monitoring, and update practices they could not maintain alone. But weak administrator practices, excessive permissions, poor configuration, and limited audit review can still create risk in a cloud deployment.
On-premise security can be the safer choice when an organization needs direct control and has the resources to maintain it. That means patching systems, monitoring logs, backing up data, testing recovery, reviewing access, and replacing unsupported components. If those duties are neglected, local ownership becomes a liability rather than a protection.
The practical question is not which label sounds more secure. It is which model your organization can operate securely, prove with evidence, and recover from when something goes wrong.
How reliability and internet outages affect physical security
Reliability has two different meanings in this discussion: cloud service availability and local continuity at the property. A cloud platform may offer distributed infrastructure and disaster-recovery options. A well-maintained on-premise system may give a property more direct local control. Neither point, by itself, tells you what happens at a specific door, gate, intercom, reader, or keypad during an internet outage.
For cloud-managed physical security, outage behavior is product-specific. It can depend on the endpoint hardware, local controller, cached permissions, power, configuration, and documented operating conditions. Some architectures allow supported local endpoints to keep making access decisions with previously synchronized permissions and then synchronize records after connectivity returns. Other functions, such as remote administration or live cloud-dependent actions, may be unavailable until service is restored.
Questions to ask about offline access
- Which readers, intercoms, controllers, and keypads can operate during a connectivity loss?
- Which credentials and permissions are cached locally, and under what conditions?
- What happens to visitor access, permission changes, event logs, and remote administration?
- What power dependencies remain at the endpoint, network equipment, and property?
- How does the system reconcile events and configuration changes after reconnection?
Do not assume every cloud or hybrid product behaves the same way. Review current documentation for the proposed configuration and test the continuity plan before depending on it. For a ButterflyMX-specific discussion, see how ButterflyMX describes cloud and on-premise security, then confirm which supported endpoints, credentials, permissions, and synchronization behaviors apply to the actual installation.
How hybrid security supports continuity and phased migration
Yes, a property can use cloud and on-premise security together. A hybrid security model may use cloud-based administration while retaining local controllers, local storage, or endpoints that operate under defined offline conditions. This can be useful when a property wants centralized management but cannot, or should not, replace every component at once.
Hybrid security is not automatically simpler. It creates a boundary between cloud responsibilities and local responsibilities, and that boundary must be designed, documented, and tested. Compatibility matters, too. A controller, reader, credential, gate, elevator interface, intercom, or building-system integration may not work with a new platform without replacement, translation, or separate operation.
A phased migration sequence
- Define security, administration, compliance, connectivity, and continuity requirements.
- Inventory servers, controllers, readers, intercoms, keypads, credentials, doors, gates, elevators, and integrations.
- Assess compatibility and identify components that must be replaced, bridged, or kept separate.
- Plan the credential transition and decide who will manage user access during the change.
- Test offline operation, recovery procedures, and synchronization in a limited deployment.
- Expand only after the pilot proves that the intended operating model works.
ButterflyMX is relevant to this discussion when a property is evaluating cloud-managed access, remote administration, and local endpoint continuity in a supported configuration. The important step is to validate the exact doors, readers, intercoms, keypads, credentials, and access rules involved. Hybrid design can reduce migration risk when components are compatible, but it should not be treated as a promise that every existing device can remain in service.
How to choose a model for each property and portfolio
The right model is the one your property can manage, afford, audit, scale, and recover. Start with the property’s actual conditions rather than with a preference for cloud or on-premise infrastructure.
- Start with the property and portfolio. Multifamily, student housing, and senior living properties may focus on resident or staff access, remote administration, and continuity at shared entrances. Commercial properties may need to account for tenants, visitors, building systems, and integrations. For commercial context, review this guide to commercial access control systems.
- Define compliance and data requirements. Identify applicable obligations, data flows, residency expectations, audit needs, and the evidence a provider or internal team must maintain.
- Inventory the installed environment. Document current servers, controllers, readers, credentials, doors, gates, elevators, intercoms, and integrations before judging whether cloud, on-premise, or hybrid deployment is realistic.
- Model total cost over time. Compare subscriptions and capital purchases alongside installation, local infrastructure, staff time, maintenance, upgrades, support, recovery, and migration. This overview of business access control systems, costs, and options can provide broader buying context.
- Evaluate operational capacity. Decide who will patch systems, approve permissions, monitor alerts, review audits, manage vendors, and run recovery procedures.
- Plan for portfolio scale. Distributed properties may benefit from centralized administration, but they still need site-level resilience, consistent governance, and a clear response process for local failures.
- Verify continuity requirements. Specify which entrances must function during an internet disruption, what power backup is required, and which administrative actions can wait until connectivity returns.
HOAs and gated communities should also think carefully about shared entrances, gates, local support capacity, and what an outage would mean for residents and visitors. For a more focused access-control comparison, see cloud versus on-premise access control for gated communities.
ButterflyMX may be a fit when a property needs cloud-managed access, remote administration, smartphone-based visitor access, and a configuration that supports the property’s continuity requirements. Residents can receive visitor calls and grant access through their smartphones, while property teams can remotely manage residents, visitors, credentials, and access. The next step is not to assume that one architecture wins. It is to compare those capabilities with your infrastructure, policies, compliance needs, and outage plan.
Frequently asked questions
What should a property ask a cloud security provider before signing a contract?
Ask for a clear breakdown of shared responsibilities, including access controls, monitoring, patching, incident response, backups, recovery, data location, audit evidence, and outage behavior. The right questions depend on the service model, property systems, and obligations that apply to your organization.
Does ISO/IEC 27001 certification make a security deployment compliant?
No. ISO/IEC 27001:2022 concerns an information security management system, while compliance with HIPAA, GDPR, PCI-DSS, or another obligation depends on the applicable requirements, certificate scope, data flows, provider controls, and your own configuration and procedures.
How should a property calculate total cost for cloud and on-premise security?
Calculate total cost by including implementation, subscriptions, servers, local infrastructure, staffing, maintenance, patching, upgrades, support, backups, recovery, downtime exposure, and migration. A subscription fee and a purchase price alone do not provide a useful comparison.
What should a property verify about offline access before choosing a cloud system?
Verify which supported endpoints cache permissions, which access events continue locally, which administrative functions require connectivity, and how data synchronizes after reconnection. Offline behavior is product-specific and should be confirmed for the proposed configuration.
The best choice between cloud security and on-premise security is the model your property can govern, maintain, audit, recover, and scale with confidence. Compare responsibility, total cost, compliance needs, infrastructure compatibility, and offline continuity together instead of treating the hosting model as the answer.
If cloud-managed access and local endpoint continuity fit your requirements, talk with ButterflyMX about the access, infrastructure, and continuity needs of your property.
Get your free quote!
Fill in the form below, and we'll email you right back.
Want a free quote?
Fill in the form below, and we'll email you right back.
You’ll be redirected shortly...